





Anthropic
Official Anthropic publications (system cards, research and threat-intel posts)
Anthropic
Claude Mythos hacks better than almost any human, too dangerous for general release
01 / THE ORIGINAL CLAIM
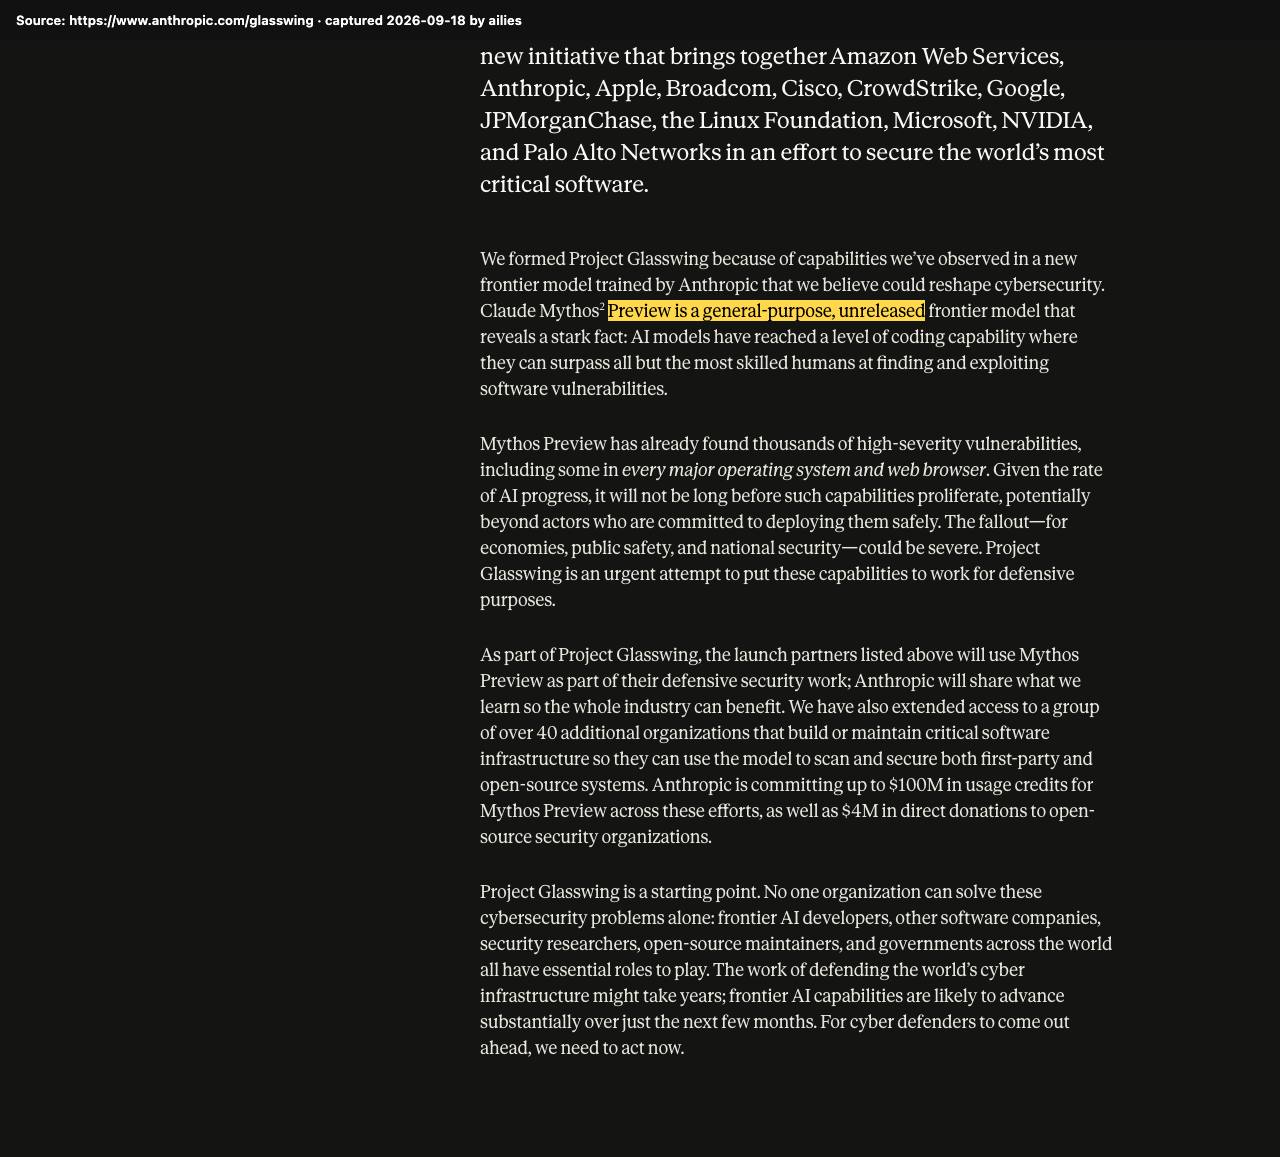
“Claude Mythos Preview is a general-purpose, unreleased frontier model that reveals a stark fact: AI models have reached a level of coding capability where they can surpass all but the most skilled humans at finding and exploiting software vulnerabilities. … The fallout—for economies, public safety, and national security—could be severe. … We do not plan to make Claude Mythos Preview generally available”
Anthropic ·
02 / THE REALITY CHECK
Overhyped'Too dangerous for general release', then a Mythos-class model went public 63 days later. Of 23,000+ findings, one was confirmed exploited in the wild.
1 of 23,000+ (126 became CVEs), VulnCheck, Jul 2026
03 / FOLLOW THE EVIDENCE
What actually happened.
-
01
Apr 7, 2026: Anthropic limited Mythos Preview to 11 launch partners (AWS, Apple, Google, Microsoft and others) plus 40+ critical-software organizations and committed up to $100M in usage credits. It said it did not plan to make Mythos Preview generally available, but that its 'eventual goal' was to let users deploy Mythos-class models safely at scale.
anthropic.com ↗ -
02
Apr 7, 2026: Security firm AISLE found eight of eight small, cheap models, one with 3.6B active parameters costing $0.11 per million tokens, spotted Mythos's flagship FreeBSD bug. The caveat: the models were handed the isolated vulnerable function plus architectural context.
aisle.com ↗ -
03
Apr 13, 2026: The UK AI Security Institute found Mythos was the first model to complete its 32-step cyber range end to end (3 of 10 attempts). The ranges had no active defenders, and AISI said it could not say whether Mythos could attack well-defended systems.
aisi.gov.uk ↗ -
04
Jun 9, 2026: Anthropic launched Claude Fable 5, 'a Mythos-class model that we've made safe for general use'. Its classifiers route cyber, bio and distillation queries to Claude Opus 4.8, and Anthropic says they trigger in under 5% of sessions. Access was suspended on June 12 and restored on July 1.
anthropic.com ↗ -
05
Jun 12, 2026: The suspension followed a US export-control directive citing a possible jailbreak of Fable 5's cyber safeguards, the first known US use of export controls against a specific frontier model. It covered foreign nationals, but Anthropic cut off all customers.
gtlaw.com ↗ -
06
Jul 29, 2026: VulnCheck found that Glasswing's 23,000+ findings had produced 126 published CVEs, with just one confirmed exploited in the wild.
infosecurity-magazine.com ↗ -
07
Sep 9, 2026: VulnCheck's review of Anthropic's disclosure ledger counted 26,153 findings, of which 2,736 had reached disclosure, 202 were patched and 245 were withdrawn. Claude rated 91.5% high or critical severity versus maintainers' 61.3%.
darkreading.com ↗ -
08
Anthropic's Linux exploit demos started from 100 already-known CVEs. Mythos picked 40, succeeded on 'more than half', and Anthropic 'selected two' to document.
red.anthropic.com ↗ -
09
AISI gave each cyber-range attempt up to 100M tokens and imposed no penalties for actions that would trigger security alerts. Performance was still rising at that budget.
aisi.gov.uk ↗ -
10
May 11, 2026: curl's lead developer Daniel Stenberg reported that a Mythos scan's five 'confirmed' curl vulnerabilities came down to one low-severity CVE: three false positives and one 'just a bug'.
daniel.haxx.se ↗
How the test was set up
From the lab's own technical record and outside reviews. Each line is sourced.
- Task given
- Explicitly directed: Claude Code was prompted with a paragraph that 'essentially amounts to "Please find a security vulnerability in this program."' red.anthropic.com ↗
- Safeguards
- AISI tested it when 'explicitly directed and given network access'. Neither source says whether safeguards were on. aisi.gov.uk ↗
- Prompting
- Claude first ranked each file 1–5 for bug likelihood. One agent was then assigned per file, and a final Mythos agent kept only bugs it judged 'real and interesting'. red.anthropic.com ↗
- Attempts
- OpenBSD: 'a thousand runs', under $20,000, for the top bug plus 'several dozen more findings'. FFmpeg: 'several hundred runs' for roughly $10,000. red.anthropic.com ↗
- Environment
- Internet-isolated containers holding the source code. Firefox exploits hit a test harness 'without the browser's process sandbox or other defense-in-depth mitigations'. red.anthropic.com ↗
- Who ran it
- 'a small team of researchers on our staff' over several weeks. The highest-severity bugs went to 'professional human triagers' before disclosure. red.anthropic.com ↗
- What the headline left out
- 'Thousands' of severe bugs was an extrapolation. Contractors reviewed 198 reports and matched Claude's severity exactly in 89%; 'fewer than 1%' were patched. red.anthropic.com ↗
Why it was overhyped
The bug-finding was real. The UK AI Security Institute confirmed Mythos Preview completed its 32-step attack range (3 of 10 tries, with no active defenders), and Mozilla fixed 271 Firefox bugs it found. The 'severe fallout' framing didn't hold, though. Anthropic released Fable 5, a Mythos-class model behind safety classifiers, on June 9, 2026. By late July VulnCheck counted one of 23,000+ Glasswing findings confirmed exploited in the wild, and Claude had rated 91.5% of the disclosed findings high or critical, versus 61.3% by maintainers. Small, cheap open models also spotted the flagship FreeBSD bug when handed the vulnerable function. A US export-control directive briefly suspended Fable 5 over a possible jailbreak of its cyber safeguards.
What outside experts said
“We took the specific vulnerabilities Anthropic showcases in their announcement, isolated the relevant code, and ran them through small, cheap, open-weights models. Those models recovered much of the same analysis.”
“My personal conclusion can however not end up with anything else than that the big hype around this model so far was primarily marketing.”
Inspect the original source capture
Evidence
- Mozilla: Firefox 150 fixed 271 vulnerabilities found with Mythos Preview blog.mozilla.org ↗
- Anthropic (May 2026): 90.6% of 1,752 checked open-source findings were valid; 75 of 530 disclosed high/critical bugs patched anthropic.com ↗
- Unauthorized Discord group accessed Mythos via a vendor environment from launch day techcrunch.com ↗
- VulnCheck (Jul 2026): 1 Glasswing finding confirmed exploited in the wild infosecurity-magazine.com ↗
- Anthropic Frontier Red Team: scaffold, run counts and costs, 198-report human validation red.anthropic.com ↗
- Daniel Stenberg: Mythos scan of curl yielded one low-severity CVE daniel.haxx.se ↗